Why “HaveIBeenPwned” Belongs in Your Security Program
“There’s a website called Have I Been Pwned, maintained by Troy Hunt. You can enter your email address and see if it’s been involved in a breach. If your email has been around for a while, it’s probably been breached. That’s not catastrophic. What matters is whether you reused passwords.” Eric Brown Most security teams […]
Loop Prompting: A Technique for Getting More Out of LLMs
Most practitioners run one prompt, read the output, and move on. For drafting emails or summarizing a document, that is fine. For anything that requires actual analytical depth, it is the wrong approach. A single LLM pass gives you the first reasonable answer, not the best one. Loop prompting is how you fix that. What […]
The Numbers Behind the Curtain

A few weeks ago I flew myself down to Orlando for CoachCon 2026, a two day gathering of entrepreneurs built around a single idea: thinking about thinking. Dan Sullivan hosted. The keynotes came from Angus Fletcher, author of Primal Intelligence, and Alison Levine, team captain of the first American Women’s Everest Expedition. I planned to […]
The Vanishing Buffer
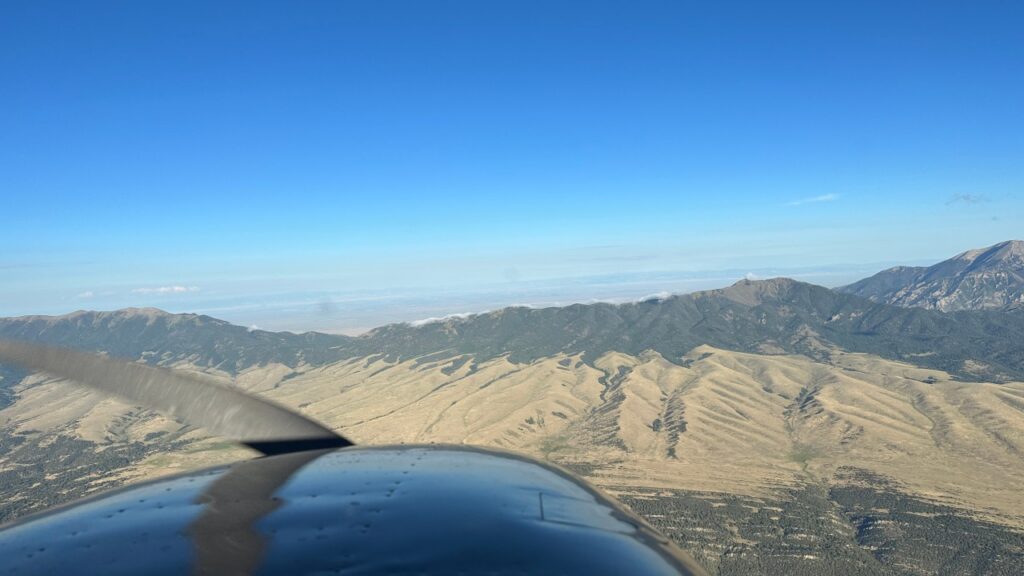
An hour over a Colorado pass, a sentence in a Google ballroom, and the disappearance of the one thing every previous technology revolution quietly handed us: time Pueblo, Colorado. Hours before sunrise. To the west, the mountains we would have to cross were still dark on dark, more shape than range. A slight breeze worked […]
Harmony, Abnormal, Proofpoint: What Matters In Email Security
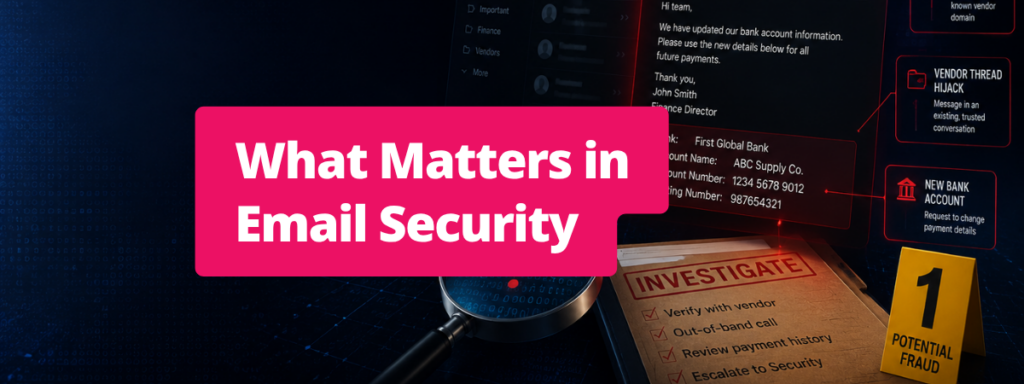
Most email security products are about as effective as eating spaghetti with a spoon. I have used quite a few. Three stand out. That number may shrink or expand because security tools change and evolve constantly. A firewall product that led the market twenty years ago should not be anywhere near a data center today. […]
When the AI Bubble Deflates, What Survives
A coworker told me today that the AI bubble is going to pop. He did not say it as a provocation. He said it with the calm of someone who has already seen how this movie ends. I feel it too. The market is going to correct. The question that stayed with me is not […]
When the Classroom Gets Hacked: The ShinyHunters Canvas Breach
Finals week is already one of the most stressful times of the academic year. For millions of students in May 2026, it got significantly harder when a threat actor group called ShinyHunters compromised Instructure, the parent company behind Canvas. With 30 million active users and 8,000+ institutional customers, Canvas serves as a central hub for […]
OSINT Isn’t Trivia. It’s Your Account Recovery Map.
Too many teams still treat OSINT as a scavenger hunt. Attackers do not. They correlate phone numbers, legacy emails, birthdays, family names, breach artifacts, and marketplace handles into a single story: how to recover, reset, or reissue access around your controls. Here is the uncomfortable truth for security leaders: enterprise exposure is often shaped by […]
Browser Extensions Are the Quiet SSO Bypass
Most organizations have a process for evaluating software. Procurement reviews, security assessments, sometimes formal vendor questionnaires. Almost none of them have a process for evaluating what browser extensions their employees are running. That gap is exactly what this campaign exploits. Researchers at Socket documented 108 malicious Chrome extensions sharing a single command-and-control backend, collectively installed […]
What The FCC Router Ban Means For Security Leaders
Why This Matters Most teams treat consumer routers as commodity hardware. The FCC’s latest move challenges that assumption — blocking new foreign-made consumer routers from U.S. markets on national security grounds. The rationale is credible. State actors like Volt Typhoon have used small office and home office routers as staging points for intrusion, surveillance, and […]